How AI-Optimized Cloud Hosting Guarantees Business Stability
Hardware-Level Seclusion in 2026 Virtual Server Environments
The standard for virtual personal server security in 2026 has actually moved from software-based firewalls to hardware-enforced isolation. As data breaches became more advanced early in the decade, the market approached Confidential Computing. This technology uses Trusted Execution Environments (TEEs) to encrypt information while it is being processed in the system memory. In 2026, any high-performance hosting solution that does not have silicon-level encryption is considered obsolete. This shift makes sure that even if a hypervisor is jeopardized, the information residing within private virtual makers remains encrypted and inaccessible to unapproved actors.
Hardware service providers have presented specialized directions in 2026 processors that particularly manage memory tagging. This prevents typical exploits like buffer overflows and use-after-free vulnerabilities at the physical level. For companies handling sensitive info, these 2026 requirements supply a layer of certainty that was formerly difficult. Memory seclusion is no longer a luxury feature however a foundational requirement for any server instance. Those who prioritize security in Asia Virtual Solutions Server regularly verify that their companies use 2026-grade chipsets with active memory encryption enabled by default.
Carrying Out No Trust for High-Performance Infrastructure
The concept of a safe boundary has actually mainly vanished in 2026. Rather, No Trust Architecture (ZTA) governs how virtual servers connect within a network. Every request, whether it originates from a known internal IP or an external source, requires rigorous authentication and permission. In 2026, identity-based security has actually replaced static IP whitelisting. This means that gain access to is given based on the identity of the service or user, validated through multi-factor authentication and cryptographic certificates that turn every few minutes.
Micro-segmentation is another pillar of 2026 VPS security. By dividing the virtual network into granular sectors, administrators can contain risks before they spread out. If one server is targeted, the rest of the network remains secured due to the fact that there is no intrinsic trust between nodes. Decision-makers discovering value in Wikipedia Virtual Server Details often indicate this granular control as a factor for its prevalent adoption. 2026 systems use automatic policies to adjust these sections in real-time based on the existing danger level, guaranteeing that efficiency stays high while protection remains tight.
Identity-aware proxies have likewise become a standard part of the 2026 stack. These proxies act as a gatekeeper, checking every package not just for its destination, however for the intent and permission of the sender. This level of examination happens at the edge of the network, reducing the load on the actual VPS and preserving the high-performance standards required by modern-day applications.
Scalability and Automated Threat Mitigation
One of the most considerable developments in 2026 is the combination of artificial intelligence for real-time threat mitigation. Traditional signature-based antivirus tools are too sluggish for the speed of 2026 cyber-attacks. Modern systems use behavioral analysis to identify abnormalities in server efficiency or network traffic. If a VPS starts exhibiting uncommon outgoing traffic patterns, the 2026 security layer can instantly throttle the connection or move the instance to a quarantined "sandbox" for additional evaluation without human intervention.
This automation is connected straight to cloud scalability. When a security risk is detected, the 2026 facilities can spin up a tidy mirror of the server while the suspicious one is analyzed. This procedure makes sure zero downtime for the end-user. The capability to scale resources throughout an attack-- such as a Dispersed Denial of Service (DDoS) event-- is a hallmark of 2026 server management. Modern scrubbers can manage terabits of destructive traffic per second, straining the sound while permitting legitimate users to access the application without lag.
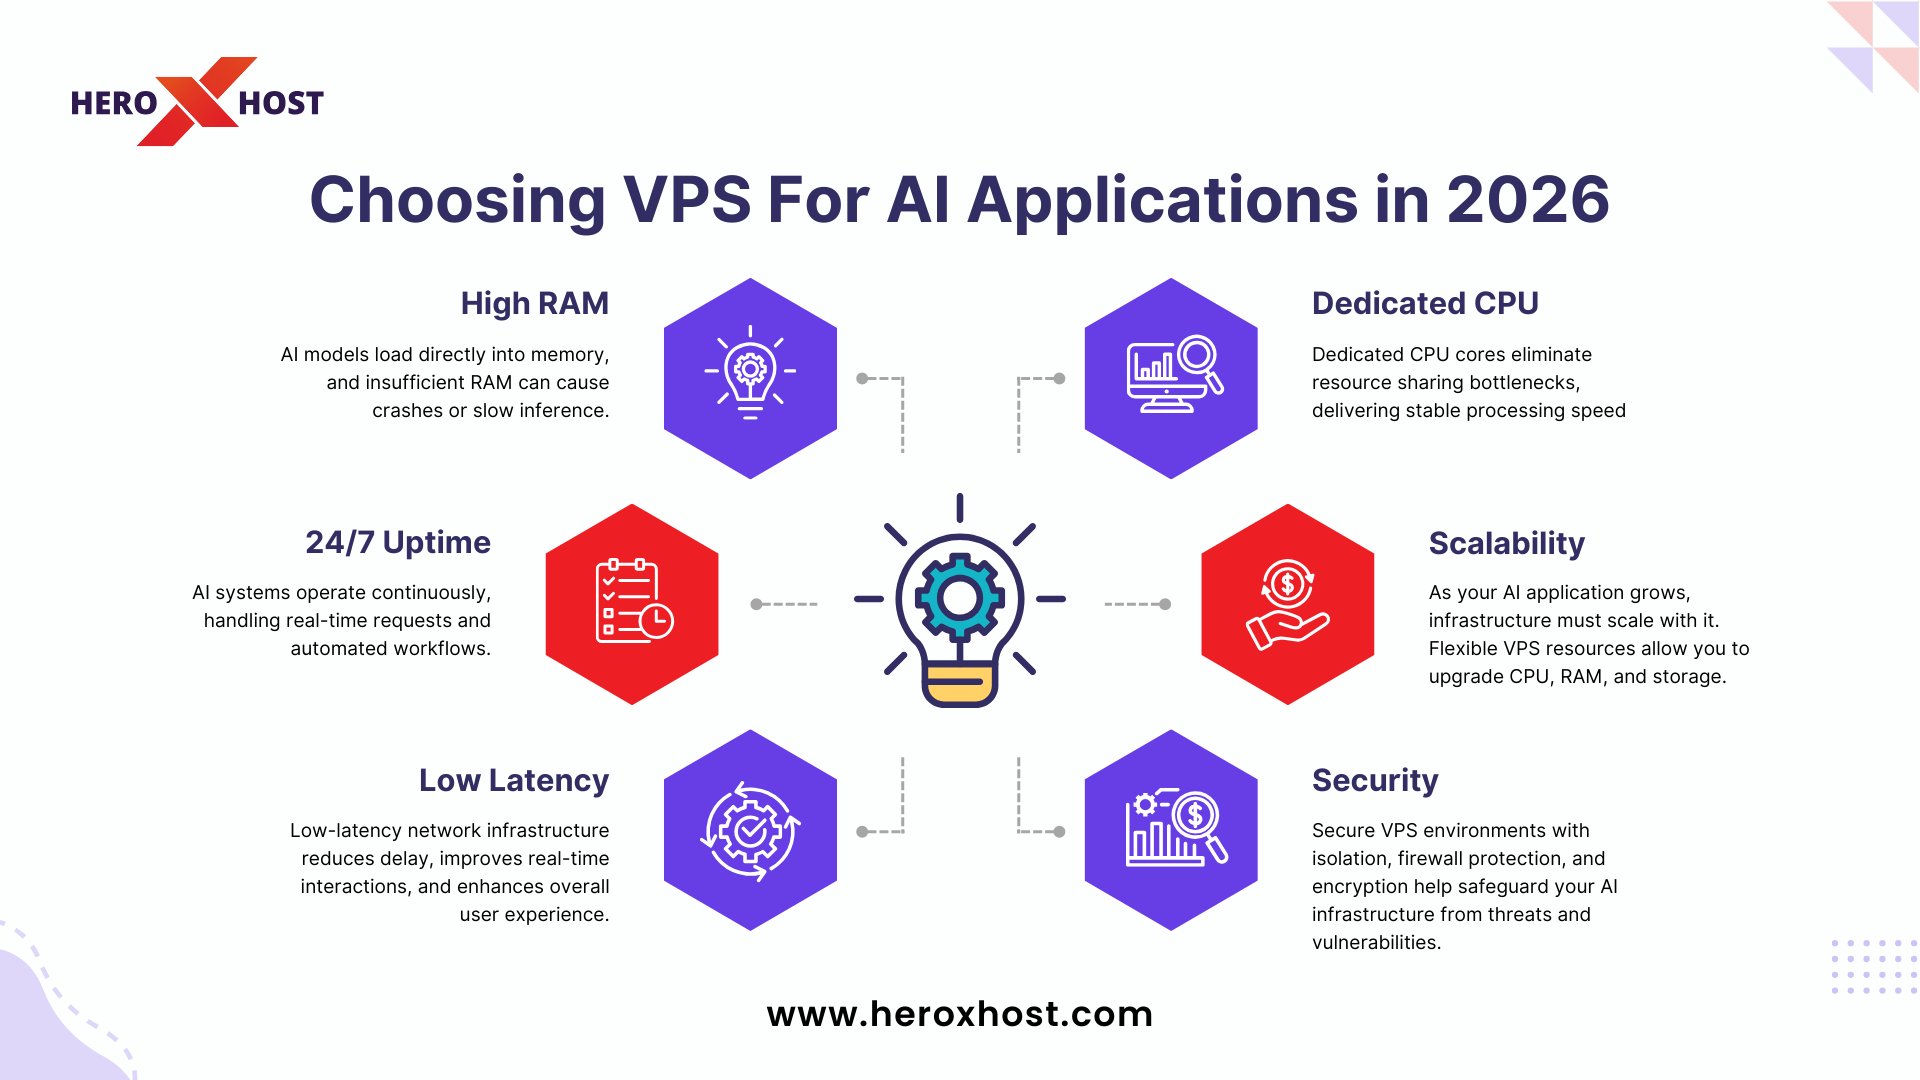
Growing need for Asia Virtual Solutions for Performance has led to the development of localized security nodes. these nodes procedure security checks more detailed to the user, which is a major consider the high-performance results seen in 2026. By unloading the heavy lifting of decryption and package evaluation to specialized edge hardware, the main VPS can dedicate its CPU and RAM to core application jobs. This separation of tasks is a crucial reason that 2026 servers are substantially faster than those from simply a few years back.
Information Sovereignty and Compliance in 2026
Regulatory requirements have become more rigid in 2026, needing accurate control over where information is stored and processed. VPS providers now use "sovereign clouds" where hardware is physically situated in particular jurisdictions and handled under local laws. Security standards in 2026 include automated compliance auditing, where the system creates real-time reports to show that data has actually not left its designated region. This is especially relevant for monetary services and doctor who should stick to stringent 2026 personal privacy requireds.
File encryption keys are no longer managed by the company in many 2026 setups. "Bring Your Own Secret" (BYOK) and "Hold Your Own Secret" (HYOK) models are the norm. This ensures that even if a federal government or a 3rd party subpoenas the hosting service provider, the data stays unreadable due to the fact that the supplier does not have the secrets. This level of autonomy is a major part of the 2026 security requirement, providing users complete ownership over their digital properties.
As we look at the 2026 environment, the focus is on a multi-layered defense. From the physical silicon to the automatic network policies and the user-controlled file encryption keys, every layer is developed to be independent yet collective. High-performance facilities in 2026 is defined by its ability to remain fast and responsive even while under continuous security and potential attack. The mix of hardware seclusion, zero-trust protocols, and automatic reaction systems makes the 2026 VPS a a lot more resistant choice for any modern-day business.
By adhering to these 2026 standards, companies can focus on development and development. The facilities manages the complexities of defense, permitting designers to deploy code with self-confidence. The 2026 shift toward incorporated, hardware-first security has actually created a more stable and predictable environment for everyone associated with the digital economy.